Blog

Cybersecurity analysis, threat intelligence, and IT governance insights.

Hershey's Halloween Disaster: What a Failed ERP Migration Costs in Chocolate
IT Audit7 min read

Hershey's Halloween Disaster: What a Failed ERP Migration Costs in Chocolate

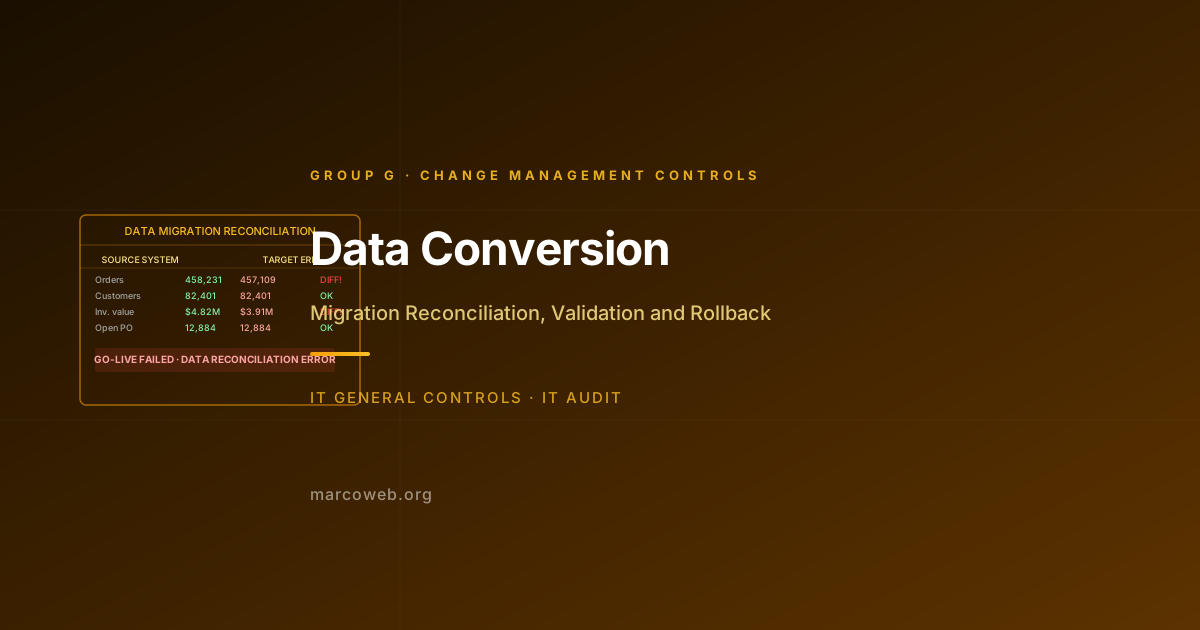
In 1999, Hershey's Foods Corporation went live with an SAP R/3 implementation on 9 July, during the peak season for Halloween candy orders. The system was not ready. Hershey's could not fill 100 million dollars worth of orders. Data conversion and migration controls exist to ensure that when you move to a new system, your business can still run.

Read more →
Data ConversionITGCHershey ERP Migration
GitLab Deleted Its Own Production Database: What Environment Separation Prevents
IT Audit7 min read

GitLab Deleted Its Own Production Database: What Environment Separation Prevents

In January 2017, a GitLab.com database administrator accidentally deleted the primary production database while attempting to remove data from a replica. The mistake cost approximately 6 hours of customer data and took 18 hours to restore from a backup that was not complete. The incident is a case study in what happens when production access is routine.

Read more →
Environment SeparationITGCGitLab Incident
TSB's IT Migration Left 1.9 Million Customers Unable to Bank for Weeks
IT Audit8 min read

TSB's IT Migration Left 1.9 Million Customers Unable to Bank for Weeks

In April 2018, TSB Bank attempted to migrate 5.4 million customer accounts from a legacy platform to a new system. The migration failed. 1.9 million customers were locked out of their accounts. Some saw other customers' balances. The failures traced back to application change management controls that were inadequate for the scale and complexity of the migration.

Read more →
Application Change ManagementITGCTSB Bank
Kaseya VSA and the Patch That Came Too Late: How Patch Management Protects 1,500 Businesses
IT Audit7 min read

Kaseya VSA and the Patch That Came Too Late: How Patch Management Protects 1,500 Businesses

On 2 July 2021, the REvil ransomware group exploited zero-day vulnerabilities in Kaseya VSA to push ransomware to up to 1,500 businesses through their managed service providers. Kaseya was already working on patches. They were not deployed before the attack. Patch management is not just a technical process: it is a race with a deadline.

Read more →
Patch ManagementITGCKaseya VSA
Knight Capital Lost $440 Million in 45 Minutes Because One Server Was Not Updated
IT Audit8 min read

Knight Capital Lost $440 Million in 45 Minutes Because One Server Was Not Updated

On 1 August 2012, a software deployment error at Knight Capital Group triggered an automated trading loop that generated $440 million in losses before humans could stop it. The failure was not in the code. It was in the change management process that allowed eight production servers to be updated without confirming all eight had been updated.

Read more →
Change ManagementITGCKnight Capital
The Access That Nobody Reviewed: How Accumulated Entitlement Becomes Fraud Risk
IT Audit7 min read

The Access That Nobody Reviewed: How Accumulated Entitlement Becomes Fraud Risk

Application access reviews are the periodic process of certifying that every active user in a finance, payroll, or ERP system still needs the access they have. When reviews are skipped, rubber-stamped, or incomplete, former employees retain access, role creep accumulates, and segregation of duties violations persist undetected.

Read more →
Application Access ReviewsITGCUser Certification
The Bupa Employee Who Downloaded 500,000 Customer Records and Sold Them
IT Audit7 min read

The Bupa Employee Who Downloaded 500,000 Customer Records and Sold Them

In 2017, a Bupa Global employee with broad database access downloaded the health insurance data of half a million customers and attempted to sell it. Application database access controls determine whether a single authorised user can reach every record in your finance and health systems, or only the records they need.

Read more →
Application Database AccessITGCBupa Breach
The Sage Insider Used an Internal Login to Steal 280 Businesses' Payroll Data
IT Audit7 min read

The Sage Insider Used an Internal Login to Steal 280 Businesses' Payroll Data

In 2016, a Sage Group employee used unauthorised internal application credentials to access the payroll and HR data of approximately 280 UK businesses. Application privileged access controls, specifically who holds superuser and administrator roles in finance and HR systems, are the controls that determine whether a single malicious insider can reach every record in the system.

Read more →
Application Privileged AccessITGCERP Superuser
When SWIFT Payments Have No Individual Owner: The Bangladesh Bank Heist
IT Audit7 min read

When SWIFT Payments Have No Individual Owner: The Bangladesh Bank Heist

In 2016, attackers sent fraudulent SWIFT payment messages from Bangladesh Bank and stole USD $81 million. The SWIFT terminal operated with limited individual attribution controls. In finance and ERP systems, generic and shared accounts are not just an audit issue: they are a fraud enabler.

Read more →
Application Generic AccountsITGCShared Accounts
Five Months After He Left Cisco, He Deleted 16,000 WebEx Accounts
IT Audit7 min read

Five Months After He Left Cisco, He Deleted 16,000 WebEx Accounts

A former Cisco engineer's cloud application access was never revoked after his resignation. Five months later, he logged in to AWS and deleted virtual machines serving 16,000 WebEx Teams customers. Application termination controls are not optional. They are the last line of defence against the access you forgot to close.

Read more →
Application TerminationITGCAccess Revocation
When HR Access Enables Tax Fraud: The UPMC Insider Breach
IT Audit7 min read

When HR Access Enables Tax Fraud: The UPMC Insider Breach

At UPMC, the personal data of 62,000 employees was stolen through the HR and payroll system by an insider with excessive access. The data was used to file fraudulent tax returns. Application new user access controls determine who reaches what, and whether that combination can be used for harm.

Read more →
Application New User AccessITGCHR System
JBS Foods Paid $11 Million Because Their ERP Had No MFA
IT Audit7 min read

JBS Foods Paid $11 Million Because Their ERP Had No MFA

In 2021, the world's largest meat processor paid USD $11 million in ransomware to protect operations that feed millions. The attack entered through weak authentication on remote access into their production ERP environment. Application authentication is not an afterthought. It is the first line of defence for your most sensitive business data.

Read more →
Application AuthenticationITGCERP Security
Wirecard's Fraud Required Access That Nobody Ever Challenged
IT Audit8 min read

Wirecard's Fraud Required Access That Nobody Ever Challenged

The EUR 1.9 billion Wirecard fraud was one of the largest accounting scandals in German corporate history. The employees who maintained the fraudulent records had access to financial systems that was never reviewed, never challenged, and never revoked. Access reviews are the periodic question: should this person still have this access?

Read more →
Access ReviewsITGCUser Access Review
Twitter's God Mode: How Privileged Access Became a $120,000 Bitcoin Scam
IT Audit8 min read

Twitter's God Mode: How Privileged Access Became a $120,000 Bitcoin Scam

In July 2020, a teenager convinced Twitter employees to hand over access to an internal admin tool that could control any account on the platform. Obama, Biden, Musk, and Apple were among the victims. Privileged access management is the control that limits the blast radius when an insider is compromised.

Read more →
Privileged AccessITGCPAM
The Ubiquiti Insider Used the Company's Own Admin Credentials to Rob It
IT Audit7 min read

The Ubiquiti Insider Used the Company's Own Admin Credentials to Rob It

A Ubiquiti employee used shared cloud admin credentials to steal gigabytes of data, then posed as an anonymous hacker demanding a ransom. When everyone knows the password, nobody can be held accountable. Generic and shared accounts are the accountability gap that auditors close.

Read more →
Generic AccountsITGCShared Credentials
He Was Fired on a Friday. His Credentials Still Worked on Monday.
IT Audit8 min read

He Was Fired on a Friday. His Credentials Still Worked on Monday.

Christopher Dobbins was terminated by Stradis Healthcare and used retained credentials to delete thousands of records needed to ship personal protective equipment during a global pandemic. Access termination is not an HR process. It is a security control.

Read more →
TerminationITGCAccess Revocation
Network Segmentation and VPN for Critical Infrastructure
Cybersecurity8 min read

Network Segmentation and VPN for Critical Infrastructure

In critical infrastructure a network breach is not a data problem, it is a physical one. Here is why segmentation is the control that keeps a compromised laptop away from a turbine, and why the VPN meant to protect the network is so often the way in.

Read more →
Critical InfrastructureNetwork SegmentationVPN
LastPass Proves That Penetration Testing Must Cover Your Cloud Environment
IT Audit8 min read

LastPass Proves That Penetration Testing Must Cover Your Cloud Environment

LastPass was breached twice in 2022. The second breach exploited a DevOps engineer's home computer to reach cloud backups that held encrypted vaults for 33 million users. Periodic security assessments of the cloud environment should have identified the path. They did not.

Read more →
Periodic Security AssessmentITGCPenetration Testing
How a Flat Network Let Attackers Hide in Marriott for Four Years
IT Audit8 min read

How a Flat Network Let Attackers Hide in Marriott for Four Years

When Marriott acquired Starwood in 2016, they inherited a compromised network. Because the two environments were poorly segmented, attackers moved freely for four years. Network Architecture is the control that determines how far a breach can travel.

Read more →
Network ArchitectureITGCNetwork Segmentation
SolarWinds and the Firewall Rules Nobody Reviewed
IT Audit8 min read

SolarWinds and the Firewall Rules Nobody Reviewed

The SolarWinds SUNBURST attack compromised 18,000 organisations. The malware called home for months. Egress filtering and network security controls should have caught it. Here is what was missing and what auditors check.

Read more →
Network Security ControlsITGCFirewall
Understanding the Cost of Data Breaches
Cybersecurity6 min read

Understanding the Cost of Data Breaches

Key insights from IBM's Cost of a Data Breach report: healthcare leads at $10.1M per breach, while AI platforms, DevSecOps, and incident response teams can significantly cut costs.

Read more →
Data BreachIBMCost Analysis
Boss of The SOC V3 Timeline
Tutorial6 min read

Boss of The SOC V3 Timeline

A chronological account of the BOTSv3 security incident on 20 August 2018, categorised by MITRE ATT&CK tactics, from initial access and phishing through to exfiltration and a Memcached DDoS attack.

Read more →
MITRE ATT&CKBOTSv3Incident Response
Exploring Zero-Day Vulnerabilities
Cybersecurity5 min read

Exploring Zero-Day Vulnerabilities

A vendor-based analysis of zero-day vulnerabilities from 2006 to 2023, revealing which companies are most associated with exploitable weaknesses, and what organisations can learn from the patterns.

Read more →
Zero-DayVulnerabilitiesMicrosoft
Governance: A Cybersecurity Lifeline for SMEs
Cybersecurity4 min read

Governance: A Cybersecurity Lifeline for SMEs

How cybersecurity governance frameworks help small and medium enterprises identify, assess, and manage risks, and why the most impacted businesses in Australia are often the ones with the least protection.

Read more →
GovernanceSMECybersecurity
ITGC Audit Tool

Streamline Your IT General Controls Audits

The RACM ITGC SaaS platform helps audit professionals manage IT General Controls assessments, from risk and control mapping to workpaper generation and evidence tracking.