Cybersecurity · IT Governance · Digital Reports

Cyber Threats Don't Wait.
Neither Should You.

In-depth cybersecurity analysis, threat intelligence, and IT governance insights from Marco Cavani, helping professionals understand and manage digital risk.

Featured Report

Hershey's Halloween Disaster: What a Failed ERP Migration Costs in Chocolate
IT Audit7 min read

Hershey's Halloween Disaster: What a Failed ERP Migration Costs in Chocolate

In 1999, Hershey's Foods Corporation went live with an SAP R/3 implementation on 9 July, during the peak season for Halloween candy orders. The system was not ready. Hershey's could not fill 100 million dollars worth of orders. Data conversion and migration controls exist to ensure that when you move to a new system, your business can still run.

Read more →
Free · IT Audit Training

Learn the reasoning, not just the checklist

Short lessons with knowledge checks covering design versus operating effectiveness, sampling, and evidence that holds up under review. Free, no sign-up.

Start learning →

Latest from the Blog

View all →
GitLab Deleted Its Own Production Database: What Environment Separation Prevents
IT Audit7 min read

GitLab Deleted Its Own Production Database: What Environment Separation Prevents

In January 2017, a GitLab.com database administrator accidentally deleted the primary production database while attempting to remove data from a replica. The mistake cost approximately 6 hours of customer data and took 18 hours to restore from a backup that was not complete. The incident is a case study in what happens when production access is routine.

Read more →
Environment SeparationITGCGitLab Incident
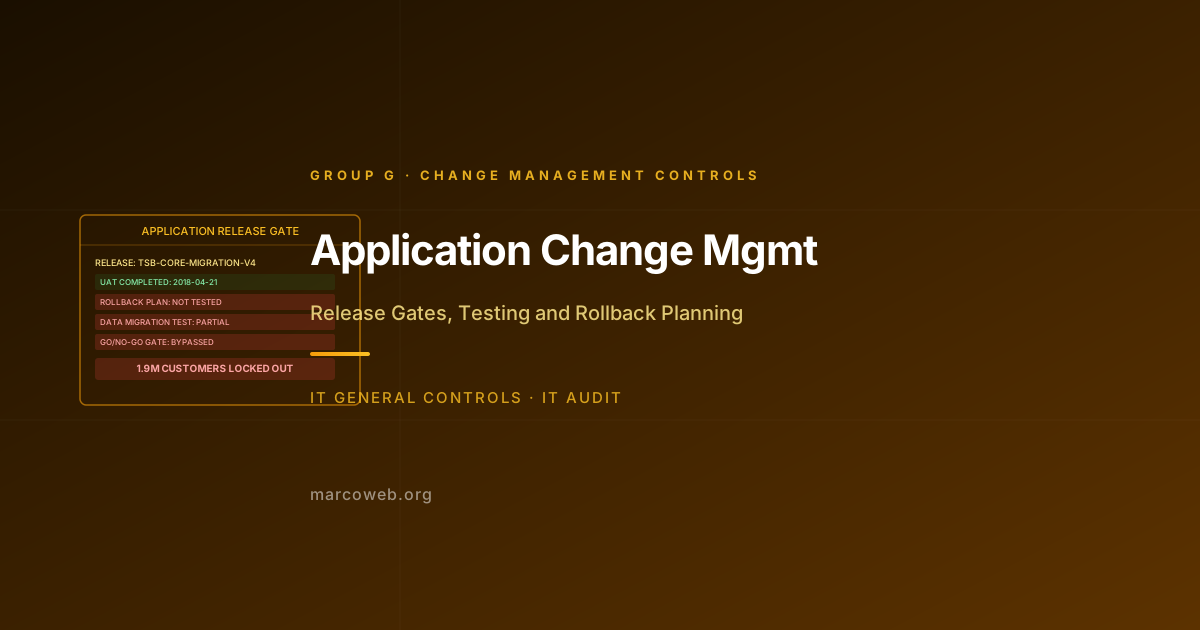
TSB's IT Migration Left 1.9 Million Customers Unable to Bank for Weeks
IT Audit8 min read

TSB's IT Migration Left 1.9 Million Customers Unable to Bank for Weeks

In April 2018, TSB Bank attempted to migrate 5.4 million customer accounts from a legacy platform to a new system. The migration failed. 1.9 million customers were locked out of their accounts. Some saw other customers' balances. The failures traced back to application change management controls that were inadequate for the scale and complexity of the migration.

Read more →
Application Change ManagementITGCTSB Bank
Kaseya VSA and the Patch That Came Too Late: How Patch Management Protects 1,500 Businesses
IT Audit7 min read

Kaseya VSA and the Patch That Came Too Late: How Patch Management Protects 1,500 Businesses

On 2 July 2021, the REvil ransomware group exploited zero-day vulnerabilities in Kaseya VSA to push ransomware to up to 1,500 businesses through their managed service providers. Kaseya was already working on patches. They were not deployed before the attack. Patch management is not just a technical process: it is a race with a deadline.

Read more →
Patch ManagementITGCKaseya VSA
Knight Capital Lost $440 Million in 45 Minutes Because One Server Was Not Updated
IT Audit8 min read

Knight Capital Lost $440 Million in 45 Minutes Because One Server Was Not Updated

On 1 August 2012, a software deployment error at Knight Capital Group triggered an automated trading loop that generated $440 million in losses before humans could stop it. The failure was not in the code. It was in the change management process that allowed eight production servers to be updated without confirming all eight had been updated.

Read more →
Change ManagementITGCKnight Capital

Digital Reports

View all →
Critical Infrastructure Report: The DP World Port Shutdown and 30,000 Stranded Containers
Digital Report10 min read

Critical Infrastructure Report: The DP World Port Shutdown and 30,000 Stranded Containers

In November 2023, a cyberattack forced DP World Australia to take its port operations offline for four days, stranding 30,000 containers at four major Australian ports. The incident demonstrated that a single managed logistics provider's security posture could be leveraged to disrupt 40 percent of Australia's container port capacity.

Read more →
Critical InfrastructureDP WorldMaritime
Critical Infrastructure Report: WannaCry and the NHS, When Ransomware Hit the National Health Service
Digital Report10 min read

Critical Infrastructure Report: WannaCry and the NHS, When Ransomware Hit the National Health Service

On 12 May 2017, WannaCry ransomware encrypted devices across 80 NHS organisations in England, forcing the cancellation of at least 19,000 appointments and procedures. This report examines how a nation-state-developed exploit became a criminal weapon and what it exposed about patch management and network segmentation in public health infrastructure.

Read more →
Critical InfrastructureNHSWannaCry
Critical Infrastructure Report: The Oldsmar Water Treatment Attack and the Sodium Hydroxide Near-Miss
Digital Report10 min read

Critical Infrastructure Report: The Oldsmar Water Treatment Attack and the Sodium Hydroxide Near-Miss

On 5 February 2021, an attacker remotely accessed the control system of the Oldsmar, Florida water treatment plant and raised the sodium hydroxide concentration to 111 times the safe level. An alert operator noticed the cursor moving and reversed the change. This near-miss exposed the open remote access vulnerabilities common in small water utilities across the US.

Read more →
Critical InfrastructureWater TreatmentOldsmar
Critical Infrastructure Report: The Ukraine Power Grid Attack, the First Confirmed Cyberattack to Cut Electricity
Digital Report11 min read

Critical Infrastructure Report: The Ukraine Power Grid Attack, the First Confirmed Cyberattack to Cut Electricity

On 23 December 2015, a coordinated cyberattack by the Sandworm group cut power to approximately 225,000 customers in western Ukraine. It was the first confirmed cyberattack to cause an electricity outage. This report examines the attack chain, the operational technology vulnerabilities it exploited, and what it established for the security of power grid infrastructure globally.

Read more →
Critical InfrastructureUkrainePower Grid
Healthcare Incident Report: The Medibank Breach and the Weaponisation of Health Data
Digital Report10 min read

Healthcare Incident Report: The Medibank Breach and the Weaponisation of Health Data

In October 2022, REvil-linked actors exfiltrated the health insurance records of 9.7 million Australians from Medibank Private. When the company refused to pay the ransom, the attackers published customers' most sensitive medical data online. This report examines the breach, the control failures, and what happens when health data becomes a coercion instrument.

Read more →
HealthcareMedibankHealth Data
Financial Services Incident Report: The Latitude Financial Breach and 14 Million Records Through a Service Provider
Digital Report9 min read

Financial Services Incident Report: The Latitude Financial Breach and 14 Million Records Through a Service Provider

In March 2023, attackers used stolen employee credentials from a service provider to access Latitude Financial's systems, ultimately stealing 14 million customer records including 7.9 million identity document numbers. This report examines the largest confirmed data theft in Australian history, the systemic third-party access failure, and the insurance and consumer finance sector's data retention exposure.

Read more →
Financial ServicesLatitude FinancialThird-Party Breach
Legal Sector Incident Report: The HWL Ebsworth Breach and the Law Firm as a Government Data Aggregator
Digital Report9 min read

Legal Sector Incident Report: The HWL Ebsworth Breach and the Law Firm as a Government Data Aggregator

In April 2023, ALPHV/BlackCat ransomware exfiltrated 4 terabytes of data from HWL Ebsworth, one of Australia's largest law firms, including data belonging to 65 federal government agency clients. This report examines how law firms function as unintended data aggregators for their clients, and why the legal sector's cybersecurity posture creates systemic risk for governments and corporations alike.

Read more →
LegalHWL EbsworthALPHV BlackCat
Telecom Incident Report: The Optus Breach and the Unauthenticated API That Exposed 9.8 Million Australians
Digital Report9 min read

Telecom Incident Report: The Optus Breach and the Unauthenticated API That Exposed 9.8 Million Australians

In September 2022, an unauthenticated API endpoint allowed an attacker to systematically enumerate and download the personal records of 9.8 million current and former Optus customers. This report examines the architectural failure, the identity document exposure it created, and what the telecommunications sector's data obligations mean for ITGC controls.

Read more →
TelecommunicationsOptusAPI Security
Government Incident Report: The Australian Parliament House Network Breach and the Nation-State Threat to Democratic Institutions
Digital Report9 min read

Government Incident Report: The Australian Parliament House Network Breach and the Nation-State Threat to Democratic Institutions

In February 2019, three weeks before the Australian federal election, the Australian Signals Directorate disclosed that the Parliament House network had been breached by a sophisticated state actor. This report examines the threat context, the ITGC implications for government networks, and the broader challenge of defending democratic institutions from nation-state espionage.

Read more →
GovernmentAustralia ParliamentState-Sponsored
Mining Incident Report: Norsk Hydro, LockerGoga, and the Aluminium Smelter That Ran on Paper
Digital Report9 min read

Mining Incident Report: Norsk Hydro, LockerGoga, and the Aluminium Smelter That Ran on Paper

In March 2019, LockerGoga ransomware encrypted Norsk Hydro's global IT systems, forcing aluminium smelters to switch to manual operations and costing the company approximately USD $71 million. This report examines how a credential compromise became a production shutdown, and what IT/OT convergence means for mining sector cybersecurity controls.

Read more →
MiningNorsk HydroLockerGoga
Pharmaceutical Incident Report: Merck, NotPetya, and the $1.3 Billion Cost of an Uninsured Cyberwar
Digital Report9 min read

Pharmaceutical Incident Report: Merck, NotPetya, and the $1.3 Billion Cost of an Uninsured Cyberwar

In June 2017, the NotPetya wiper destroyed 30,000 of Merck's computer systems, halted pharmaceutical manufacturing, and resulted in estimated losses of USD $1.3 billion. This report examines the incident, its specific implications for regulated pharmaceutical environments, and the ITGC control failures that amplified the damage.

Read more →
PharmaceuticalMerckNotPetya
Scattered Spider: The Casino Hacks
Digital Report14 min read

Scattered Spider: The Casino Hacks

In 2023, a hacking group known as Scattered Spider or UNC3944 made headlines for its sophisticated cyberattacks on two of the largest casino companies in the United States: Caesars Entertainment and MGM Resorts International.

Read more →
CybersecurityRansomwareSocial Engineering
Information Security Analysis for Western Power
Digital Report25 min read

Information Security Analysis for Western Power

A comprehensive assessment and strategic roadmap for Western Power, addressing key challenges in cybersecurity, insider threats, and climate change resilience for one of Australia's largest electricity distributors.

Read more →
CybersecurityCritical InfrastructureInformation Security

Stay ahead of cyber threats

Get the latest cybersecurity reports, threat intelligence, and IT governance insights delivered straight to your inbox. No spam. Unsubscribe any time.

No spam. Unsubscribe at any time.

ITGC Audit Tool

Streamline Your IT General Controls Audits

The RACM ITGC SaaS platform helps audit professionals manage IT General Controls assessments, from risk and control mapping to workpaper generation and evidence tracking.